

Somewhere in a Google Sheet right now, a crypto marketing lead is coloring a cell green because a wallet connected forty minutes after someone clicked a paid ad. That's the whole chain of evidence: a click, a gap, a connect. No signature, no confirmed transaction, nothing that survives a hard question from project founders.
It gets reported upward as a conversion anyway, because the dashboard only has one column for "it worked." That habit is the problem this piece exists to fix. We'll build a proper event-state taxonomy for paid crypto campaigns, work through what you can and can't legally attach to a wallet address, and show what an honest attribution report looks like when it admits its own limits rather than papering over them.
Why Web3 Conversion Is Not One Event
A wallet connect is not a conversion. It's an attempt at one, and treating it as the finish line is how teams end up reporting a number nobody can defend under scrutiny.
Web2 attribution had it comparatively easy: a click, a form fill, a purchase confirmation, all fired by the same server, all logged in the same session. Web3 breaks that chain into pieces that happen on different systems, at different speeds, sometimes not at all.
Here's the actual sequence, and where most tracking setups quietly turn into wishful thinking:
- Ad interaction. A click or view on the paid placement, timestamped and channel-tagged.
- Landing-page action. The visitor lands, and does something, or doesn't. Bounce is the default outcome, not the exception.
- Wallet connection attempt. They click "Connect Wallet." This is a request, not a guarantee.
- User rejection. They cancel the connection or reject a signature prompt. This happens constantly, and almost no dashboard has a column for it.
- Signed intent. A message or transaction gets signed, which proves intent, not settlement, and a signature can sit pending for minutes while the chain congests.
- Confirmed on-chain event. The transaction lands on-chain and gets confirmed. This is the only state that represents something actually happening.
A user can sign and then their transaction fails or gets dropped, and if you're only counting signatures, you've counted an event that never became real. Repeat use compounds the problem further: the same wallet connecting to three separate campaigns over a month looks, to most dashboards, like three separate people converting.
None of this is solved by better tooling alone. It's solved by naming the states and refusing to collapse them into one, which is exactly what the next section does.
Create the Event-state Taxonomy
The fix is a schema, not a spreadsheet trick. Every event needs a name, a status, a timestamp, a channel, and a small, deliberately limited set of attribution fields, no more than the analysis actually requires.
Here's an example of what that taxonomy should look like in practice:
| Event Name | Status | Timestamp | Channel | Attribution Fields |
| ad_click | fired | click time | paid_search / paid_social / display | campaign_id, click_id |
| landing_view | fired | page load | referral | campaign_id, click_id |
| wallet_connect_attempt | requested | button click | site | click_id (if present) |
| wallet_connect_rejected | rejected | rejection time | site | click_id (if present) |
| signature_requested | pending | request time | site | click_id (if present) |
| signature_confirmed | signed | signature time | site | click_id (if present) |
| onchain_tx_confirmed | confirmed | block time | chain | tx_hash, block_number |
Notice what's deliberately absent: no wallet address stored against a persistent user profile, no device fingerprint bolted on "just in case." The click_id is a short-lived, campaign-scoped token, not an identity. That's the whole discipline of this section: capture the state, not the person.
This is also where most teams reach straight for a wallet address as their join key, because it looks stable and unique. It is neither, once you consider that the same person can connect from three different wallets across three sessions.
Persisting a wallet address against ad-click data at this layer is legally fraught. It turns a marketing log into something closer to a financial dossier than a campaign report, and it's the kind of design decision likely to trigger a full data protection impact assessment rather than avoid one. Avoid it unless you have a genuine, documented reason to need identity-level granularity.
Set Consent and Data-minimization Rules
Consent has to be obtained before any attribution field beyond an anonymous click token gets stored, and it has to be specific to that purpose, not bundled into a general cookie banner nobody reads. This is the compliance minefield where most crypto campaigns lose a foot, and most guides to this topic skip the section entirely.
GDPR's Article 6 sets out six lawful bases for processing personal data, consent among them, and requires that where consent is the chosen basis, it must be granular enough that a person can agree to one purpose without agreeing to another. The European Data Protection Board has been explicit that whichever basis a controller relies on, it still has to satisfy the data minimization principle under Article 5, meaning you collect what the analysis actually needs and nothing else.
Whether a wallet address counts as personal data at all is genuinely contested, and treating it as settled either way is a mistake. The safer operating assumption, particularly once a wallet address gets correlated with an IP, a click ID, or off-chain identity data, is to treat the combination as personal data and design the minimization and retention rules accordingly.
The upshot? You need four things in place before the wallet-connect button even fires:
- Notice. Tell the user, before the wallet-connect prompt appears, what gets logged and why.
- Lawful basis. Document which Article 6 ground applies to each field you store, not the whole event stream in one blanket justification.
- Retention. Set a deletion window for click IDs and session data, and actually enforce it, rather than leaving it to grow indefinitely in a warehouse.
- Access and deletion. Build the mechanism for a user to ask what you hold and have it removed, before you need it, not after a regulator asks why you don't have one.
This is the same discipline that should sit behind any crypto PPC program touching regulated products, and it is not optional color text. Both platforms treat the category as high-risk by default: Meta requires advertisers promoting crypto trading platforms to submit a recognized regulatory license and get written permission before a single ad runs, and Google's own policy gates crypto exchanges and wallets behind certification requirements that vary by market.
If the platforms won't let you switch the ads on without paperwork, treating your own data collection as an afterthought is not a defensible position.
Use Aggregate and Modeled Reporting Carefully
Individual-level certainty is mostly unavailable in this environment. Chasing a single, clean, person-level match is like trying to pin a shadow to the wall of a moving tunnel; the honest response is to report in aggregate rather than pretend the shadow ever sat still.
Google's own consent architecture is a useful illustration of what "modeled, not observed" actually means in practice. Consent Mode translates a user's consent choices into request parameters Google's systems can read, and when a user denies consent, Google Ads can be set so that ads cookies and IDs simply aren't used for that visitor at all.
Full, granular measurement only exists once permission is actually granted. Everything before that point is estimation, not observation, and the platform is upfront about that rather than hiding it in a footnote. Advertiser-specific modeling only activates once a domain has cleared 700 ad clicks over 7 days in a given country, which tells you plainly that Google itself won't guess at the individual level below a volume threshold it trusts.
Read that the right way round: a platform built by a company with Google's engineering resources still won't claim individual-level certainty where consent hasn't been given or volume hasn't cleared its own bar. A crypto marketing team reporting wallet-connect "conversions" off a handful of clicks, with no consent signal and no confidence band attached, is making a claim with less rigour behind it than the platform running the ads is willing to make.
The practical version of this for a crypto campaign is a cohort view: of everyone who clicked this ad set this week, what proportion reached each state in the taxonomy, reported as a rate with a stated denominator, not as a headcount presented as fact. That framing survives an audit. A single "conversions: 340" number does not, because nobody asking a follow-up question will get an answer.
Connect Offline or Verified Outcomes Responsibly
Matching a confirmed on-chain event or an offline outcome back to a specific ad click is where teams are most tempted to overstate what they've actually built, and it's where the language has to be most careful. What you're describing is correlation, dressed up correctly, not identity resolution.
Chainalysis draws the same distinction from the compliance side: wallet attribution in the forensic sense is a different discipline from ad attribution, even though the two fields borrow the same word and confuse each other constantly.
If you're uploading confirmed conversions back into an ad platform, the mechanics are unambiguous about what's required. Google's guidance on uploading conversions requires that identifying customer data be normalized and hashed with SHA-256 before it ever reaches Google's systems, and only fields that actually carry personal weight, an email or a phone number, get hashed at all.
That hashing requirement exists precisely because raw personal data shouldn't leave your systems in the clear, and it's worth building the same discipline into your own wallet-to-click matching rather than treating hashing as something only the ad platform needs to worry about.
Offline conversion imports are also mid-migration. Google is moving offline and enhanced conversion uploads to its Data Manager API from June 2026, and retiring the older upload route entirely. Anyone building a pipeline that uploads verified on-chain outcomes back to Google needs to build against the destination that will still exist next year, not the one that's being switched off.
Document the matching logic itself as plainly as you'd document a database schema:
- What field is the join key, and how long does it live before it's purged.
- What proportion of attempted matches fail, and why, whether that's a cross-device session, a rejected consent state, or a signature that never confirmed.
- What gets excluded from the match entirely, and on what basis.
Building that documentation before a platform or a regulator asks for it is cheaper than building it after. The Creative Impact Group crypto PPC team treats this kind of matching-logic paper trail as part of running paid campaigns in a regulated category at all, not as an optional add-on once something goes wrong.
If you're weighing programmatic buys against search and social spend for the same budget, our guide on crypto programmatic advertising for crypto covers how the attribution problem changes shape across formats.
Build an Attribution-confidence Report
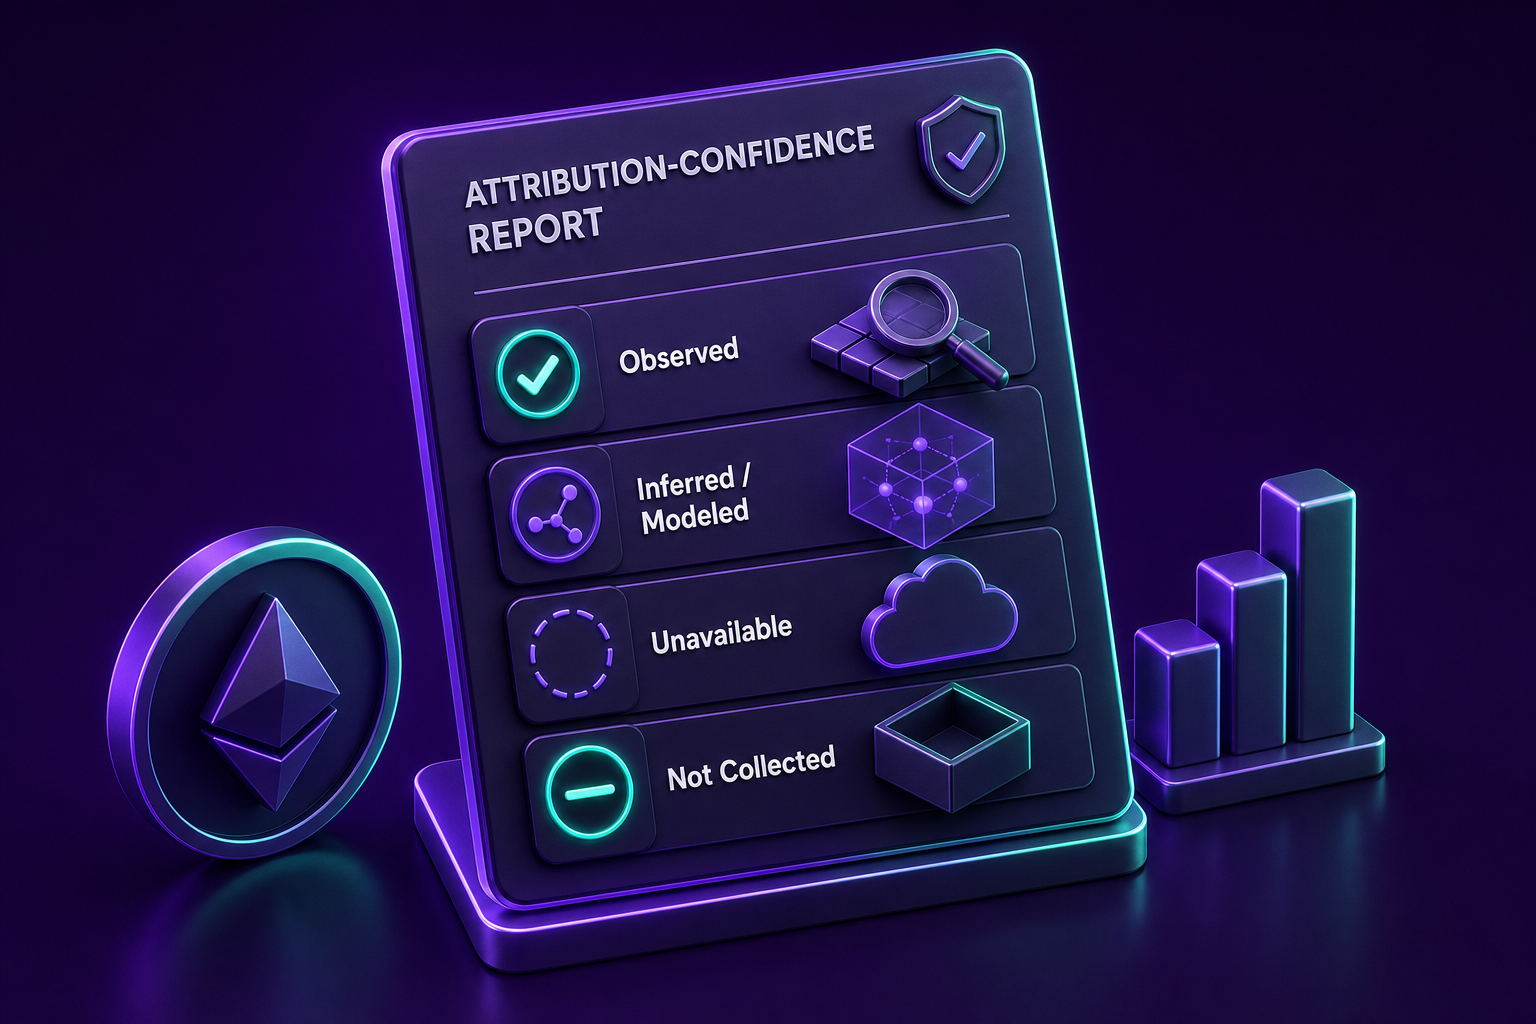
The report a stakeholder actually needs isn't a single conversion number, it's a breakdown of what's known, what's estimated, and what was never collected in the first place. That structure is more useful precisely because it's less flattering.
Here's an example of how that report should be structured:
| Category | What It Means | Example |
| Observed | Directly logged, timestamped event with a valid click token | ad_click → wallet_connect_attempt with matching click_id |
| Inferred / Modeled | Estimated via aggregate modeling, not a specific user record | Consent-denied sessions modeled in aggregate rather than tracked individually |
| Unavailable | Should exist but couldn't be captured (consent denied, session lost) | wallet_connect_rejected with no prior click_id |
| Not Collected (by design) | Deliberately excluded under the minimization rules | Raw wallet address persisted against ad-click history |
Treating a rejected signature as if it never happened is the data equivalent of sweeping evidence off the table before anyone counts it. Creative Impact Group doesn't publish a blanket match-rate figure for wallet connects tied back to paid clicks, and any agency handing you one without a campaign, a consent rate and a channel mix attached to it is handing you a marketing number, not a measurement.
Here's the honest range worth knowing before you build a target around one: trade-press analysis of on-chain attribution tools has been candid that cross-device sessions and consent settings routinely break the correlation chain between a click and a wallet, and that even dedicated attribution vendors decline to guarantee a fixed match rate because it moves with consent rates, device mix and campaign channel. That is the correct way to hold this number in your head; not as a fixed percentage, but as a range that shrinks or grows with your own consent rate.
What a real confidence report looks like for a specific campaign, at a specific consent rate, is something worth walking through against your own data rather than lifting from a case study that ran on somebody else's audience. It would show, by channel and by consent state, exactly how many events landed in each of the four rows above, not one blended headline number sitting on top of all of it.
Conclusion
Attribution in Web3 isn't a worse version of Web2 tracking, it's a genuinely different discipline, one built on states, confidence bands and documented restraint rather than a single deterministic number. Get that structure right and the report you hand your board is one that survives a hard question instead of dodging it.
That green cell in the spreadsheet from the start of this piece isn't wrong because someone made an error. It's wrong because the taxonomy underneath it never existed, so there was nothing to check it against. Build the states first, and the number in that cell becomes something you can actually stand behind. Measure Web3 acquisition without turning wallets into surveillance data, and contact Creative Impact Group to design a privacy-first attribution taxonomy before your next campaign brief goes out.
Below is a quick-reference data dictionary covering the terms and questions that come up most often once a team starts building this taxonomy for real.
FAQs
Is a wallet connection a conversion?
No. A wallet connection is a request to connect, not proof that anything happened, and treating it as a completed conversion in your crypto PPC attribution reporting overstates what you actually observed. It sits between landing-page action and signed intent in the taxonomy above, and it needs its own status field precisely because a meaningful share of connection attempts get rejected before a signature is ever requested.
Can wallet data be used for ad attribution?
Only with real caution, and only once you've worked out whether the data counts as personal information in your jurisdiction. A raw wallet address correlated with a click ID and an IP address is the kind of combination that tips into personal data territory even where a bare address alone might not, so the safer default is to treat it as such and build retention and access rights around it from day one.
What consent is required for tracking?
Specific, informed consent tied to the exact purpose, given before the data is collected, not folded into a general cookie banner. GDPR Article 6 sets out the lawful bases available, and consent has to be granular enough that a user can agree to attribution tracking without also being deemed to have agreed to something else entirely.
How should rejected signatures be recorded?
As their own event, with their own status, not silently dropped from the dataset. A wallet_connect_rejected or signature_rejected state, timestamped and channel-tagged like every other event, tells you where in the funnel people are actually walking away, which a dashboard with only a "converted" column will never show you. Our case studies page has examples of campaigns where mapping the drop-off states changed the read on which channel was actually underperforming.
Why should on-chain attribution include confidence levels?
Because a single number hides exactly the information a stakeholder needs, whether a result came from a directly observed event or an educated guess. A confidence report that separates observed, inferred, unavailable and intentionally uncollected events gives you something you can defend under a hard question, and it is the difference between a measurement and a marketing claim dressed up as one.